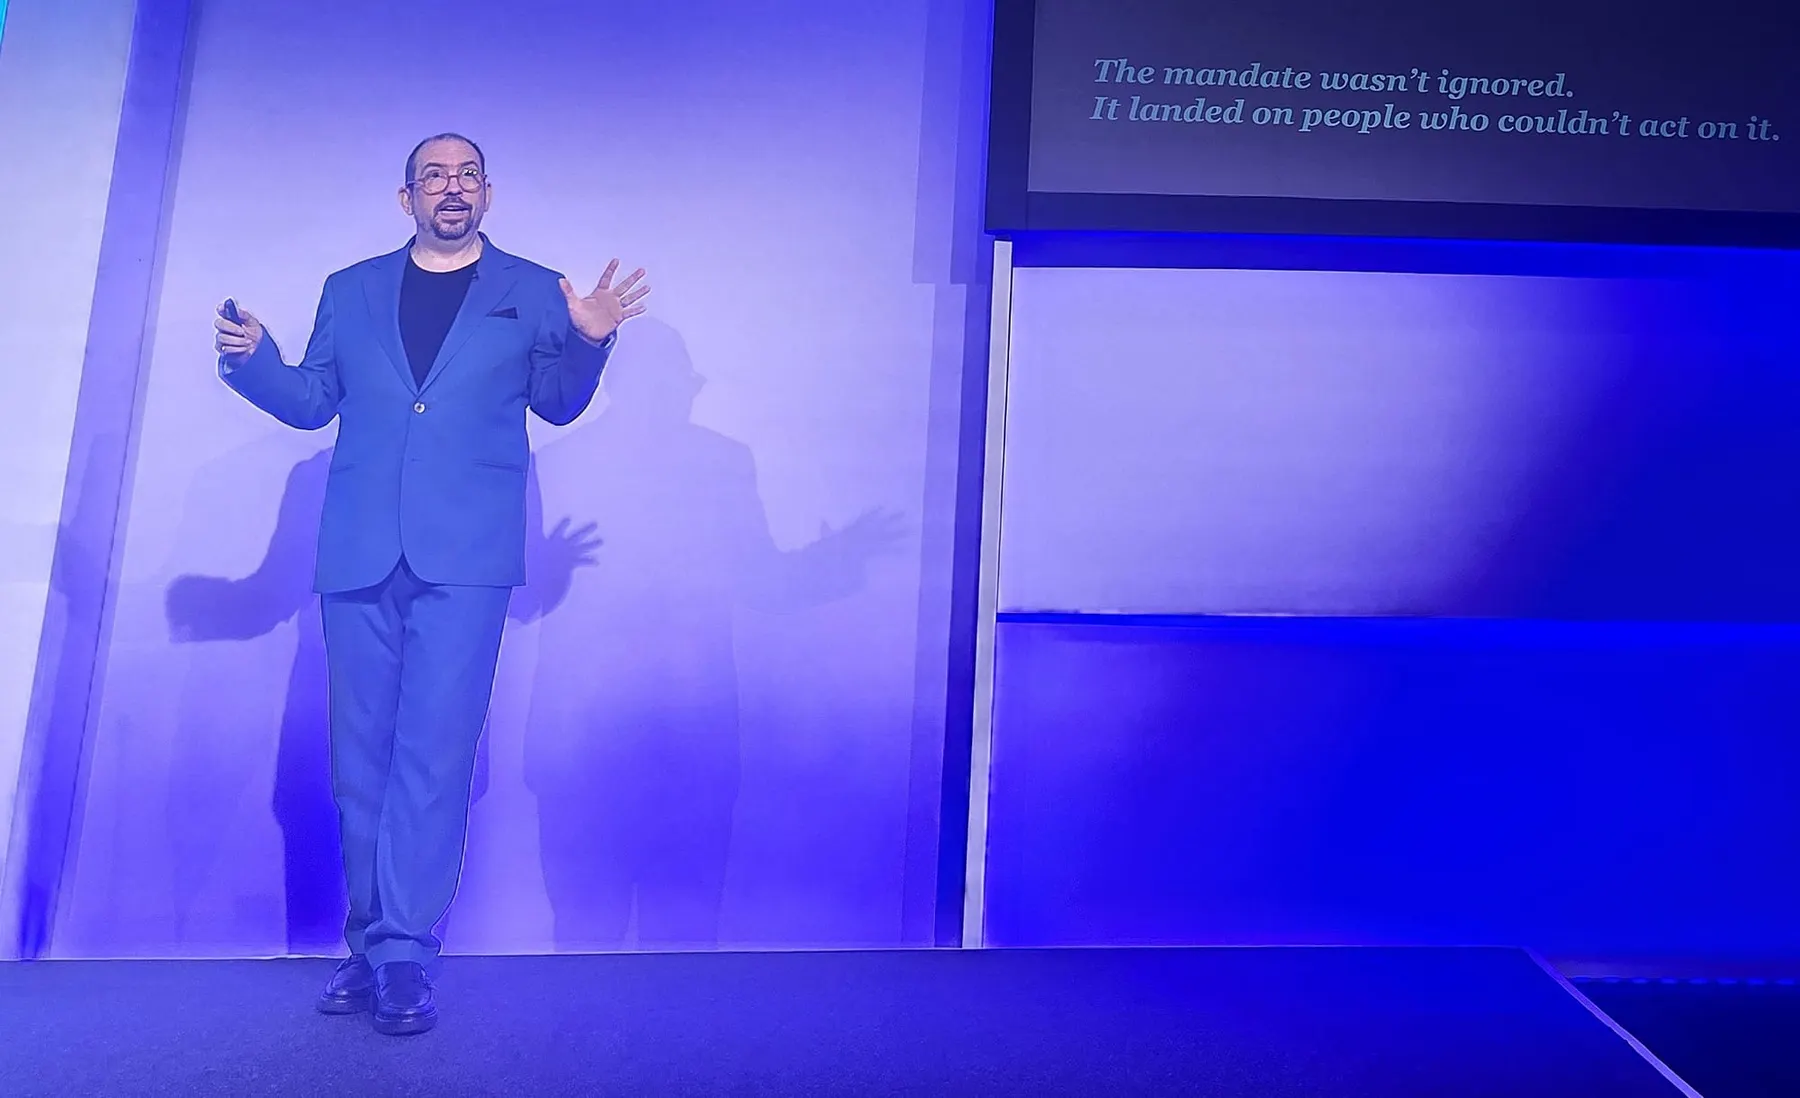
The British government’s deputy CISO, Breandán Knowlton-Hung, has spelled out in sharp detail the challenge of trying to drive cybersecurity reform from the centre of a highly federated “mess” of an organisational structure – and how it has forced his team to rethink how they wield authority from a central cybersecurity function.
Knowlton-Hung, speaking at the Gartner risk summit in London, spelled out the structural problem of government cybersecurity in a crisp synopsis for his talk: “The centre is accountable for national resilience but doesn't own the risk, hold the budgets, or run the systems. Standards flow down [but] behaviour rarely changes.”