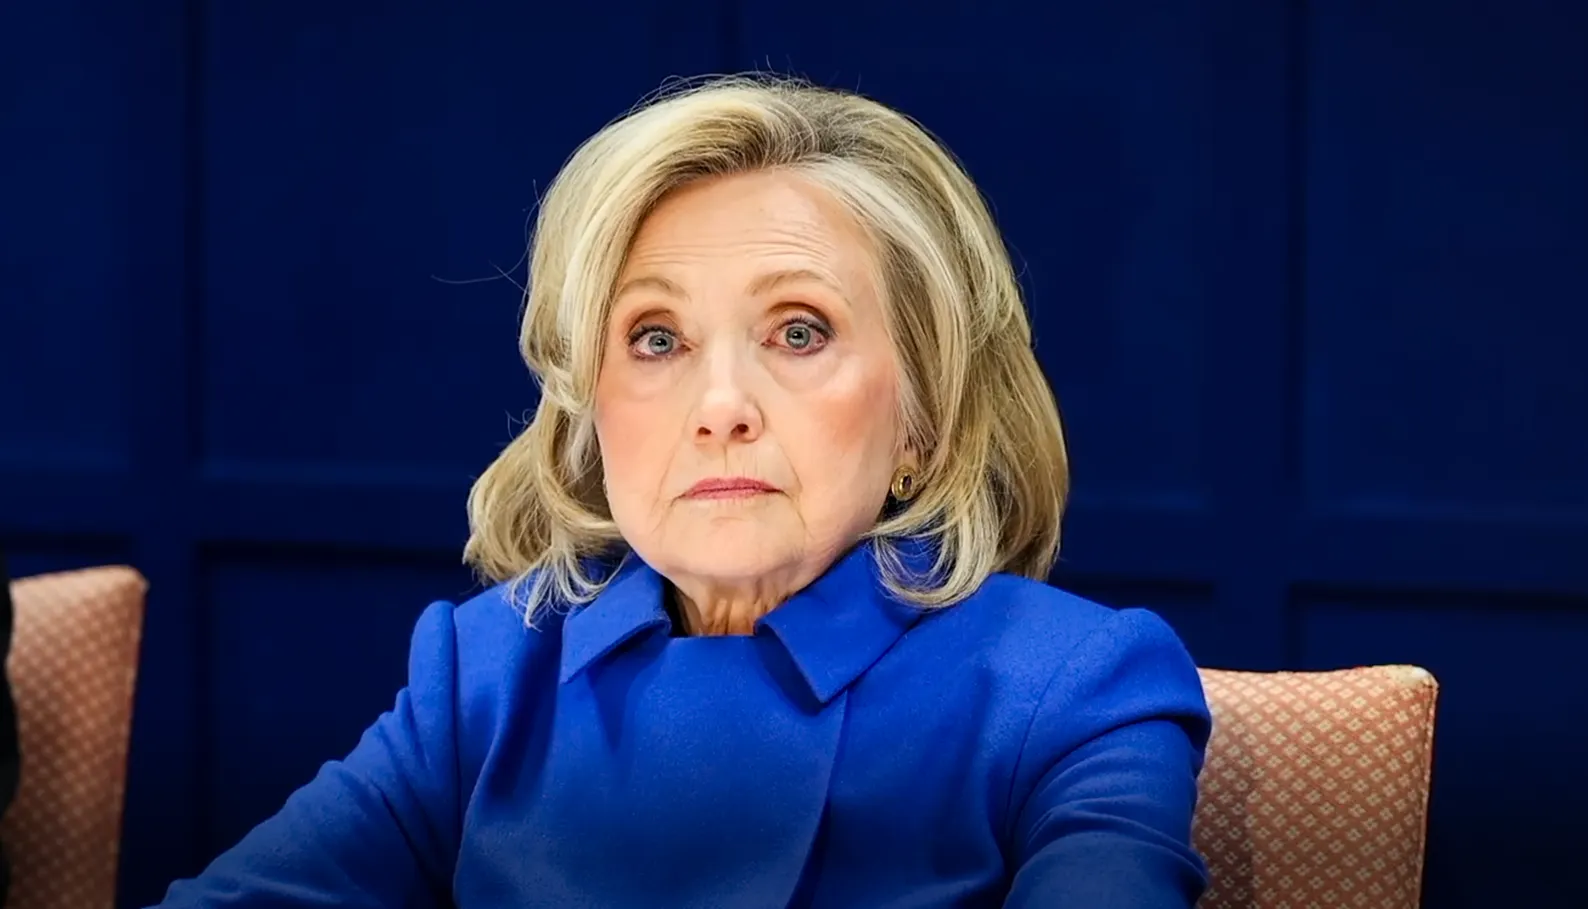
Hillary Clinton warned that open-source AI models are not an “unadulterated good” and “actually pose additional dangers" after a conversation this week with LinkedIn founder and investor Reid Hoffman at her Clinton Global Initiative meeting.
Speaking in New York on September 23, Hoffman added: “The issue is it’s a dangerous piece of technology” adding that “one-to-three people in their garage” with an open-weight model could train it to find novel attack vectors and cause major damage.
Notably, of course, all recent high-profile cyberattacks have been performed by proprietary AI models from frontier labs with poor sandboxing and deeply insufficient monitoring. There is no evidence that open-weight models present more danger.
Indeed, when Hugging Face was attacked, it had to resort to responding with China’s open-weight GLM 5.2 – as cyber guardrails in the proprietary Anthropic and OpenAI models it had access to, thwarted its ability to meaningfully use them defensively.
Hugging Face hacked: Turned to Chinese LLM for help after US models blocked Blue Team
OpenAI has yet to publish a truly meaningful post-mortem of the attacks by its agent swarms, sharing neither the prompts nor complete datasets of the actions.
As SentinelOne's Tom Hegel recently commented "Frontier labs should release a redacted, action-complete dataset after an agent incident. Not only a narrative report or private review. Once an agent reaches systems outside its developer’s environment, the evidence no longer concerns only the originating lab…”
Hugging Face co-founder Clem Delangue hit back at Clinton and Reid’s comments.
He said: “If you believe the risk is coming from 1-3 people in a garage with no money and no compute, you just don't understand this technology and haven't learned anything this summer. Risk comes from the asymmetry of capabilities created by secret labs training frontier agents and running them with massive amount of compute."
Delangue added: "Open-source is exactly the solution to this asymmetry and empowers hospitals (and any smaller orgs) to defend themselves!”
Addressing criticism of his stance on X, Delangue added: “...a few people in a garage or some small criminals, I don't think they can do something horrible without a large amount of compute. And if they try, we should try to fight them with law enforcement, not by creating massive asymmetry and concentration of power and preventing everyone to use this technology to defend themselves.”
Since its agents attacked Hugging Face, OpenAI has promised to expand monitoring and response capabilities across its research environments, including by "establishing a consistent baseline of platform-level monitoring across research environments, including IAM, networking, and control-plane activity."
US Treasury Secretary Scott Bessent responded sharply when asked about the incident on CNBC's Squawk Box on Monday.
"The Hugging Face incident, that is the responsibility of the OpenAI management, not a bunch of agents,” Bessent said, adding: “These labs need to take responsibility for themselves. They can slow down any time they want to.”
(Loose back-of-a-napkin-math suggests that the Hugging Face attack alone would have cost OpenAI tens of millions in compute. It took METR some $400,000 in OpenAI API credits over just six days just to analyse the transcript data left behind by the agents… Want to share your estimate? Pop a line to ed@thestack.technology)