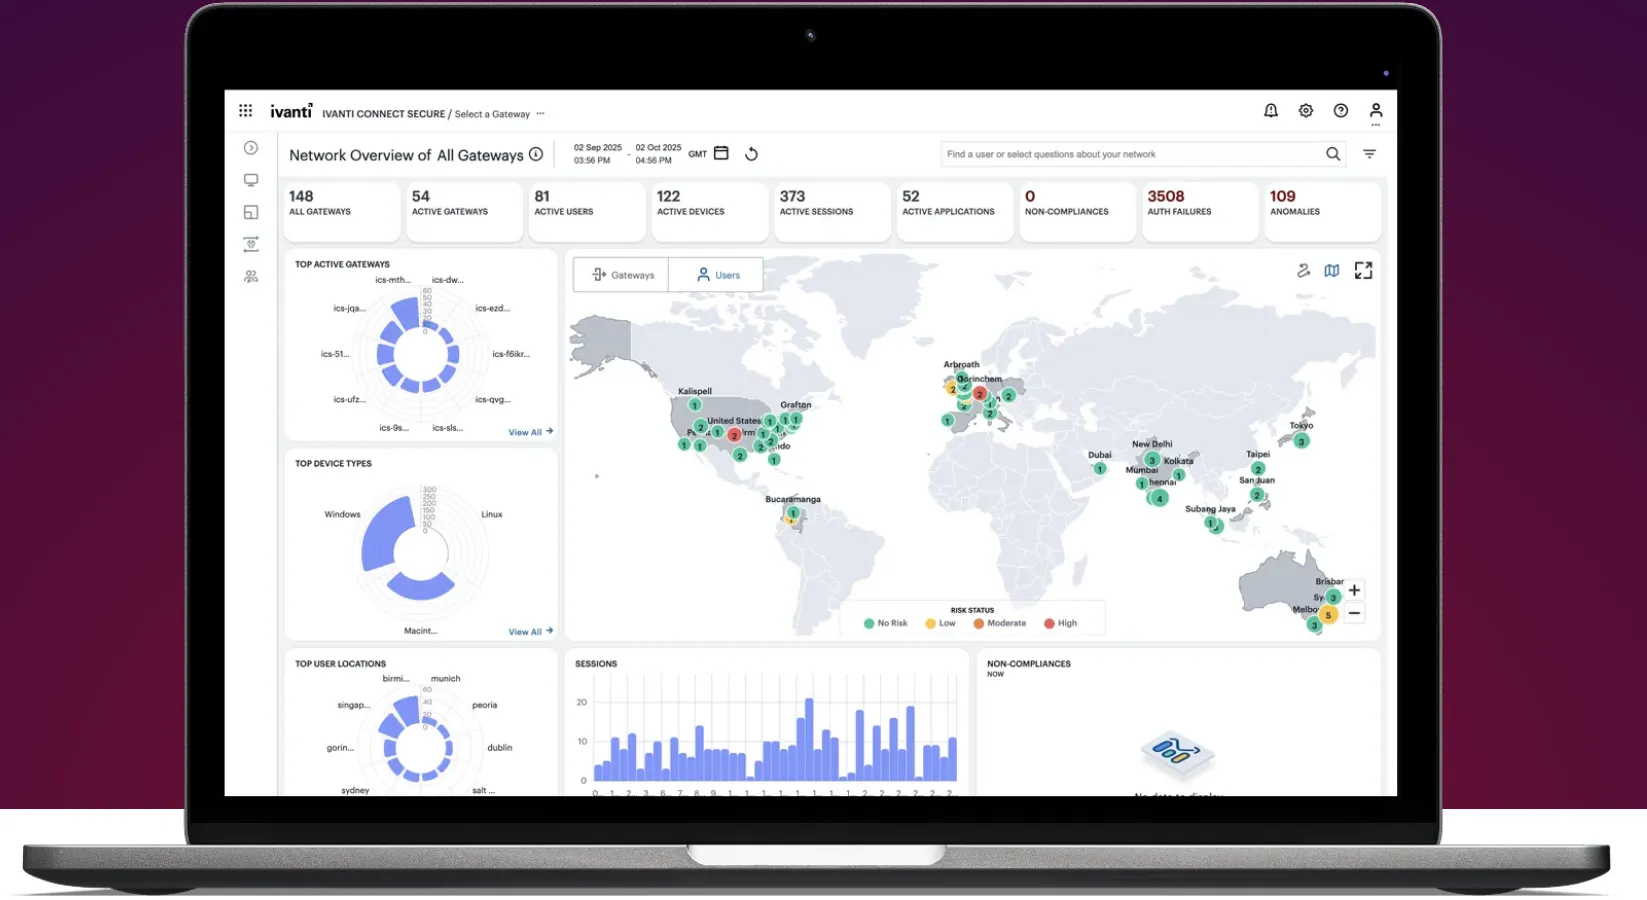
A sophisticated threat actor has been exploiting Ivanti Connect Secure VPN devices since at least early October – chaining a trio of CVEs for full pre-authentication RCE.
Ivanti today (October 29) pushed fixes for two CVEs exploited in the chain, having patched the initial authentication bypass bug, CVE-2026-104935 on October 13.
Cybersecurity company Volexity was first to spot exploitation in the wild.
It said earlier this month that the attacker appeared to be passing every command and receiving every result inside the HTTPS requests of the exploit chain itself, re-running the entire three-stage chain (auth bypass to RCE to privilege escalation) for each command they wanted to execute, and not using a dedicated C2 channel.
This appeared to be quite bespoke hands-on-keyboard activity with a choice by the attacker to pay the re-exploitation cost every time in exchange for leaving no persistent artifact. (For a defender, this means the familiar question “where’s the implant / where’s the beacon?” is a moot one. Ivanti itself noted that “there are limited indicators of compromise available,” although Volexity shared some useful detail.)
Volexity is tracking the attacker as UTA0576. It said they are “primarily focused on credential theft, data exfiltration, log tampering, and network reconnaissance.” Specifically, with access to Ivanti Connect Secure, the attacker did the following:
- "Extracted credentials stored on the ICS VPN appliance, such as domain credentials used with LDAP
- Dumped and exfiltrated limited Active Directory metadata
- Deployed a custom Kerberos tool capable of Kerberoast attacks and credential testing
- Deployed a custom Python LDAP tool to search Active Directory for LAPS local administrator passwords, BitLocker recovery keys, and password-bearing attributes via a compromised Active Directory service account
- Local DNS and host reconnaissance
- Collected ICS VPN appliance configuration data, including authentication methods
- Password spraying
- Packet capture of LDAP traffic from the compromised ICS VPN appliance
- Inspection of authentication logs to identify valid usernames"
Ivanti disclosed and pushed fixes for CVE-2026-11357 and CVE-2026-118527 (respectively a CVSS 8.8 EOP bug and a CVSS 4.3 but that lets an authenticated attacker upload files with attacker-controlled content to disk) on October 29.
It said: “At the time of discovery of exploitation, Ivanti had a fix developed for CVE-2026-104935 which was already in QA for supported versions, and we made the decision to not delay getting a fix to customers [to fix the] primary exploitation path.”
Some 26 Ivanti vulnerabilities have been added to CISA's KEV since the start of 2024. Six of them have come this year. Network appliances remain a major area of focus for threat actors.
Ivanti’s standard (not this incident-specific) guide on restoring a compromised Ivanti Connect Secure(ICS)/Ivanti Policy Secure(IPS) appliance is here. Its advisory here.
Tracking the same threat actor? Know more. Signal your thoughts to @Targett.11
Affected versions below
|
Product Name |
Affected Version(s) |
Resolved Version(s) |
Patch Availability |
|
CVE-2026-104935 | |||
|
Ivanti Connect Secure (ICS) |
25.1.1.1 and prior 25.1.2.2 and prior 22.8R2.4 and prior |
25.1.1.2 25.1.3.0, 25.1.3.1 22.8R2.5 |
Download Available in ILS |
|
CVE-2026-111357 & CVE-2026-118527 | |||
|
Ivanti Connect Secure (ICS) |
25.1.1.2 and prior 22.8R2.5 and prior |
25.1.1.3 22.8R2.6
|
Download Available in ILS
|