Updated and rewritten with more details at 21:35 BST, Sep. 27.
Citrix has confirmed ongoing exploitation of a pair of NetScaler zero days.
Its advisory comes after days of furious speculation in the cybersecurity community about an ongoing campaign against NetScaler users – and the earlier circulation by the Dutch NCSC of an TLP: Amber advisory.
The two exploited bugs have been allocated CVE-2026-88771 and CVE-2026-88772. Citrix confirmed the attacks in an advisory late Sunday.
It also shipped patches for six other vulnerabilities.
CVE-2026-88771 (CVSS 9.5) is a pre-auth RCE bug due to improper input validation. It affects all NetScaler ADC and NetScaler Gateway deployments in default configurations. CVE-2026-88772 (also CVSS 9.5) is a memory overflow bug also leading to RCE. It affects users where the DTLS configuration is enabled on NetScaler ADC or NetScaler Gateway.
The latter is enabled by default on VPN vServer.
Citrix owner Cloud Software Group “strongly urges" affected customers of NetScaler ADC and NetScaler Gateway to update, it said on Sunday.
Fixed versions:
- NetScaler ADC and NetScaler Gateway 14.1-73.37 and later.
- NetScaler ADC and NetScaler Gateway 13.1-64.23 and later.
- NetScaler ADC 14.1-FIPS 14.1-73.37 FIPS and later.
- NetScaler ADC 13.1-FIPS, 13.1-NDcPP 13.1.37.279 and later.
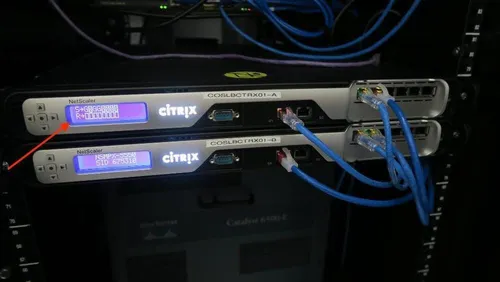
Citrix NetScaler appliances are widely used by major banks, governments and other organisations as a network gateway, VPN virtual server, ICA proxy, or for other critical network purposes depending on configuration.
The Stack understands that the bugs were proactively disclosed to Citrix by a large customer prior to their exploitation and Citrix did not push an emergency fix until attacks started. The company’s security team was said to be infuriated at the slow pace of the fixes. More to follow.
CISA commented: "Both are critical, zero-day vulnerabilities that can independently enable remote code execution. CISA has received reports and partner threat intelligence confirming that threat actors are actively exploiting these vulnerabilities globally."
Customers that suspect compromise, Citrix said, should:
Ensure:
All service account passwords and secrets stored on the NetScaler are changed on their respective systems (e.g., LDAP service accounts, RADIUS shared secrets, OAuth tokens, API Keys, SNMP community names).
All user accounts that may have been authenticated via the suspected compromised platform, including Gateway or AAA virtual servers are changed on their respective systems.
Certificates and associated private keys stored on the suspected compromised platform are revoked.
Investigate Connected Systems
Investigate all servers and systems that the NetScaler ADC had connected to for any signs of further compromise, particularly authentication servers, sensitive systems, web tier systems, and management jump hosts.
Rebuild and Restore
MPX appliances - Refer to the official guide to erase and reinstall the MPX
Affected? Have views? ed@thestack.technology or Signal @Targett.11
A blog posted on the https://sh3llc0d3.com threat intel site without authorial attribution claimed that the exploits target "defects in the proprietary native C/C++ packet processing engine (nsppe) running directly on the FreeBSD-based NetScaler operating system kernel."
The post, shared with The Stack by a respected security veteran closely tracking the incident, added that the subsequent "control flow hijack provides the adversary with immediate execution under the nobody or root service context." We could not immediately confirm this independently.
A since-deleted version of the alleged NCSC advisory posted online, suggested that “The zero-day vulnerabilities were discovered during an investigation by Citrix at customer environments following reports of disruptions… Exploitation has been identified at multiple Citrix customers worldwide. The NCSC does not currently know whether these zero-day vulnerabilities are being exploited on a widespread scale.”
“One of the vulnerabilities involves placing shellcode in memory. Similar techniques have previously been observed with critical Citrix NetScaler vulnerabilities," the Dutch NCSC allegedly said.
(When contacted on the private advisory, a spokesperson said that "we provide information and advice to organizations so that they can take appropriate measures. As you're not part of our constituency, we cannot disclose any further information at this time.")
CISA says:
Because updating Citrix NetScaler appliances can be complex and may require downtime, CISA is issuing this Alert to help organizations assess exposure, prioritize mitigation, and account for these vulnerabilities into their risk-management activities.
Given the potential consequences of successful exploitation and the fact that malicious actors are exploiting at least some of these vulnerabilities, CISA urges users and administrators to review Citrix’s advisories. If possible, users are encouraged to check for indication of compromise prior to patching. Citrix has made indicators of compromise available through NetScaler Console and published additional guidance in their recent publication, Security Bulletin for CVE-2026-88771 through CVE-2026-88778, to support organizations in assessing potential compromise. Should your organization suspect compromise, it is important to preserve forensic evidence prior to applying updates, as updates may result in loss of forensic visibility.
- Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 - Security Updates - Citrix Community
- Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771, CVE-2026-88772, CVE-2026-88773, CVE-2026-88774, CVE-2026-88775, CVE-2026-88776, CVE-2026-88777, and CVE-2026-88778
- Steps to Take if NetScaler ADC is Suspected to be Compromised
NetScaler exploitation... is worryingly regular
NetScaler appliances are regularly attacked: recent examples of vulnerabilities that have been targeted by hackers this year alone include authentication bypass bug CVE-2026-19490, and memory overflow bugs CVE-2026-8452 and CVE-2026-3055.
NetScaler appliances were also exploited at massive scale by threat groups abusing “CitrixBleed” in 2023, aka CVE-2023-4966 – a bug that let attackers grab valid session tokens from internet-facing NetScaler devices’ memory. These could be used to hijack active sessions, bypassing MFA. The likes of Boeing and the world’s largest bank, China’s ICBC were breached during that threat campaign by a ransomware group.
As The Stack noted earlier this summer, NetScaler and many other network appliances are riddled with ageing and insecure code/sometimes underlying operating systems; critics warn that similar classes of exploitable vulnerability will keep rearing their heads despite widespread industry “Secure by Design” pledges, without much more aggressive and proactive action by the companies that build, ship, and maintain this software and hardware.
Ripping and replacing NetScaler is typically not a trivially undertaken option.
Depending on deployment configuration, that can involve things like re-engineering how external and internal DNS failover mechanisms operate; auditing and recoding thousands of lines of configuration files into F5 iRules, Nginx configurations, or cloud-native load balancer rules (depending on which frying pan looks preferable to the fire); feature the risk of breaking tortuous firewall access control lists (ACLs) and generally rearchitecting AAA (Authentication, Authorisation, Auditing) policies.
The Stack keeps its security reporting free for public interest purposes. You can support our independent journalism and grab a 50% discount to tickets for our events by subscribing for $300/year.